Enterprise security at a rational price
Choose based on your number of domains and asset scale. No credit card to start. Talk to us for annual and multi-year billing.
Basic
$250 / mo
- Up to 3 root domains
- 1,500 scan credits per month
Best for small teams or startups introducing security monitoring for the first time.
Standard
$500 / mo
- Up to 10 root domains
- 15,000 scan credits per month
Best for growing teams operating multiple domains.
Business
$1,000 / mo
- Up to 30 root domains
- 37,500 scan credits per month
Best for mid-sized and larger organizations running multiple brands or services.
More than 30 root domains or need more credits? We'll build an enterprise plan that fits your scale.
What are scan credits?
Scan credits power every scan you run on Safe Intelligence. Choose the right depth for the job with two scan tiers.
Tier 1 Scan - Map your exposed assets
See what's exposed to the outside world, fast. Covers open ports, SSL certificates, DNS, and security headers.
Cost: 1 credit per scan
Tier 2 Scan - Deep vulnerability assessment
Goes deeper - pinpoints known, exploitable vulnerabilities tailored to your discovered assets. Covers CVEs, misconfigurations, exposed sensitive paths, and more.
Cost: 10 credits per scan
Need more credits?
Used up the credits in your plan? Top up anytime. Credit top-up: 1,000 credits - $200.
Scanning often? Upgrading your plan costs less per credit. Top-ups are there for when you need a quick boost. But if you're consistently running low, moving up a plan lowers your cost per credit significantly.
Common features included in all plans
Subdomain auto discovery
Automatically discovers all subdomains under your registered domains.
Port & service scanning
Identifies exposed ports and running external services.
CVE vulnerability detection
Maps known vulnerabilities automatically and evaluates their risk level.
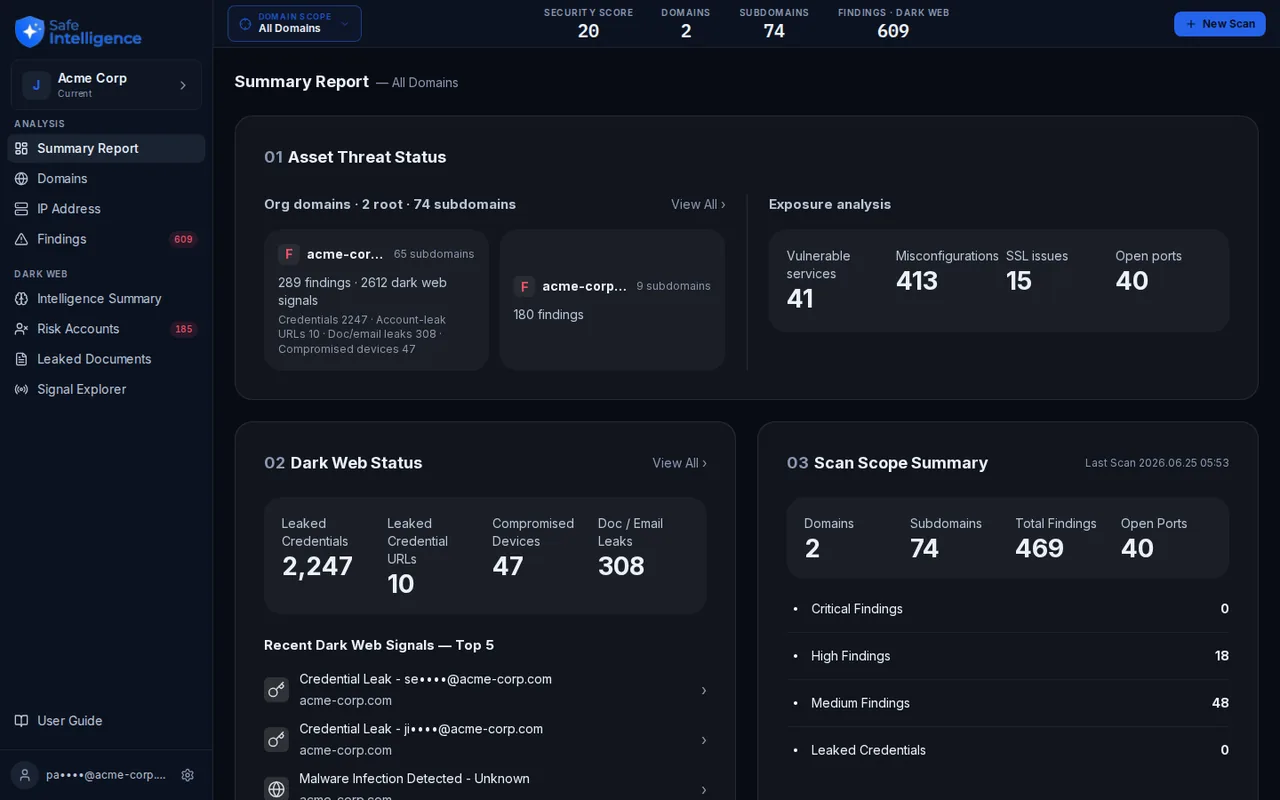
Risk management dashboard
Review and manage all discovered security risks in one place.
24/7 automated monitoring
Once configured, continuously detects new threats automatically.
Team collaboration & owner assignment
Assign discovered risks to owners and collaborate across teams.
Additional options
Dark Web Intelligence Premium $200 / domain / mo
Real-time monitoring of whether employee emails/passwords and corporate information in emails or documents are leaked and traded on the dark web. When leaks are detected, your team can review the details and respond quickly.
Dark web monitoring applies only to root domains already registered in your active plan. Domains not registered in your plan cannot be added to dark web monitoring.
Get started